Technology Behind the Experience
Intelligent, secure, and resilient technology engineered for India's financial institutions.
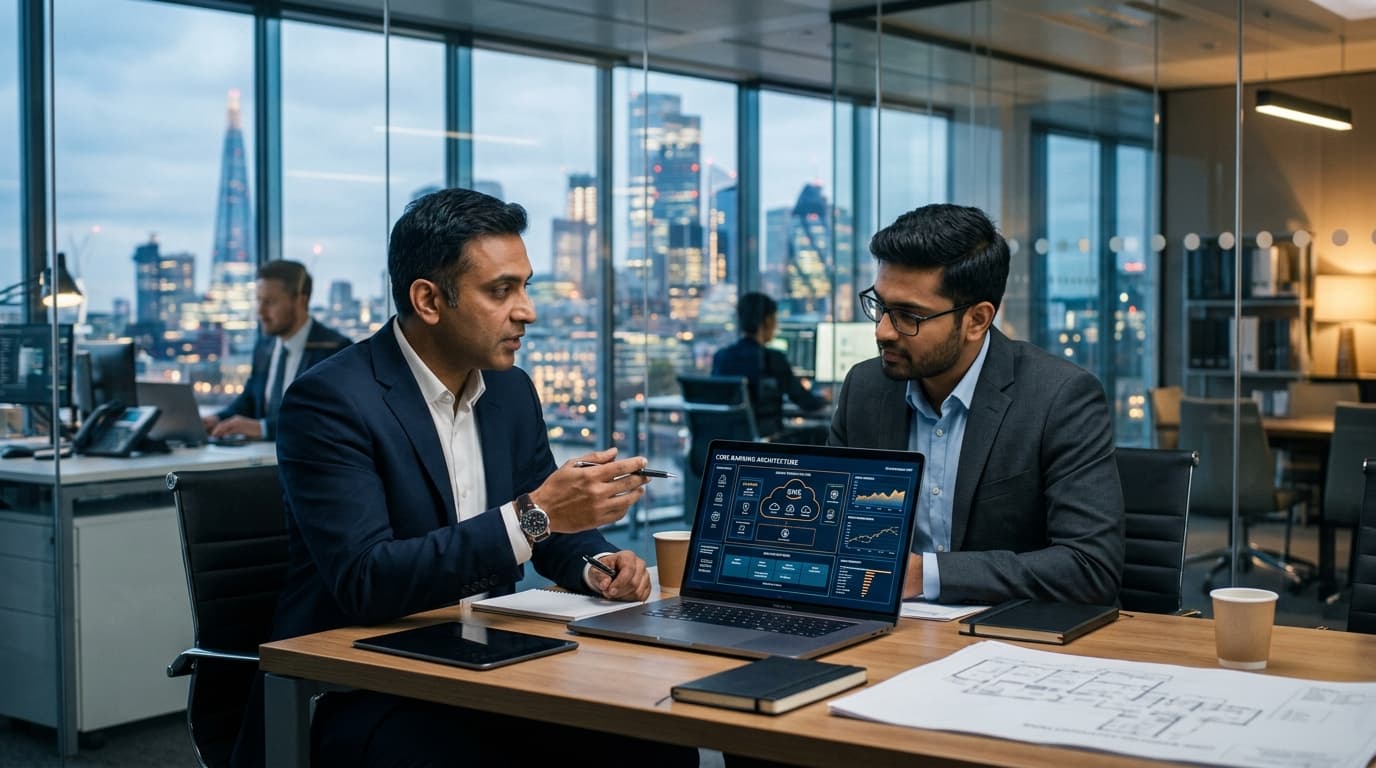
Finverge combines high-throughput transaction processing, AI document intelligence, bi-directional core banking interoperability, and institutional security to power mission-critical banking operations.
The Architecture of Certainty.
Select a pillar below to explore our core clearing and security capabilities.
Never Fear the 4:00 PM Cutoff Rush Again.
The visceral panic of closing cutoff windows simply vanishes. Thousands of branch cheque files digest in parallel without queue stalls or operator stress.
Never Fear the 4:00 PM Cutoff Rush Again.
The visceral panic of closing cutoff windows simply vanishes. Thousands of branch cheque files digest in parallel without queue stalls or operator stress.
Multi-Layered Security Architecture
Defense-in-depth framework safeguarding identity, application workflows, cryptographic keys, and continuous audit trails.
Identity & Access
Enforces zero-trust perimeter control with granular role permissions, continuous token authorization, and mandatory dual Maker-Checker approval across all critical adjustments.
Application Hardening
Shields instrument workflows with field-level snippet masking, zero-disk memory execution during OCR processing, and rigorous API gateway sanitization against injection threats.
Data & Cryptography
Guarantees end-to-end data integrity with AES-256 encryption at rest, TLS 1.3 in transit, and hardware-level PKCS#11 HSM cryptographic signing for every clearing batch.
Operations & Governance
Maintains cryptographically sealed, tamper-evident audit logs with automated day-end clearing reconciliation and seamless active-passive disaster recovery failover.
Deploy on Your Bank's Terms
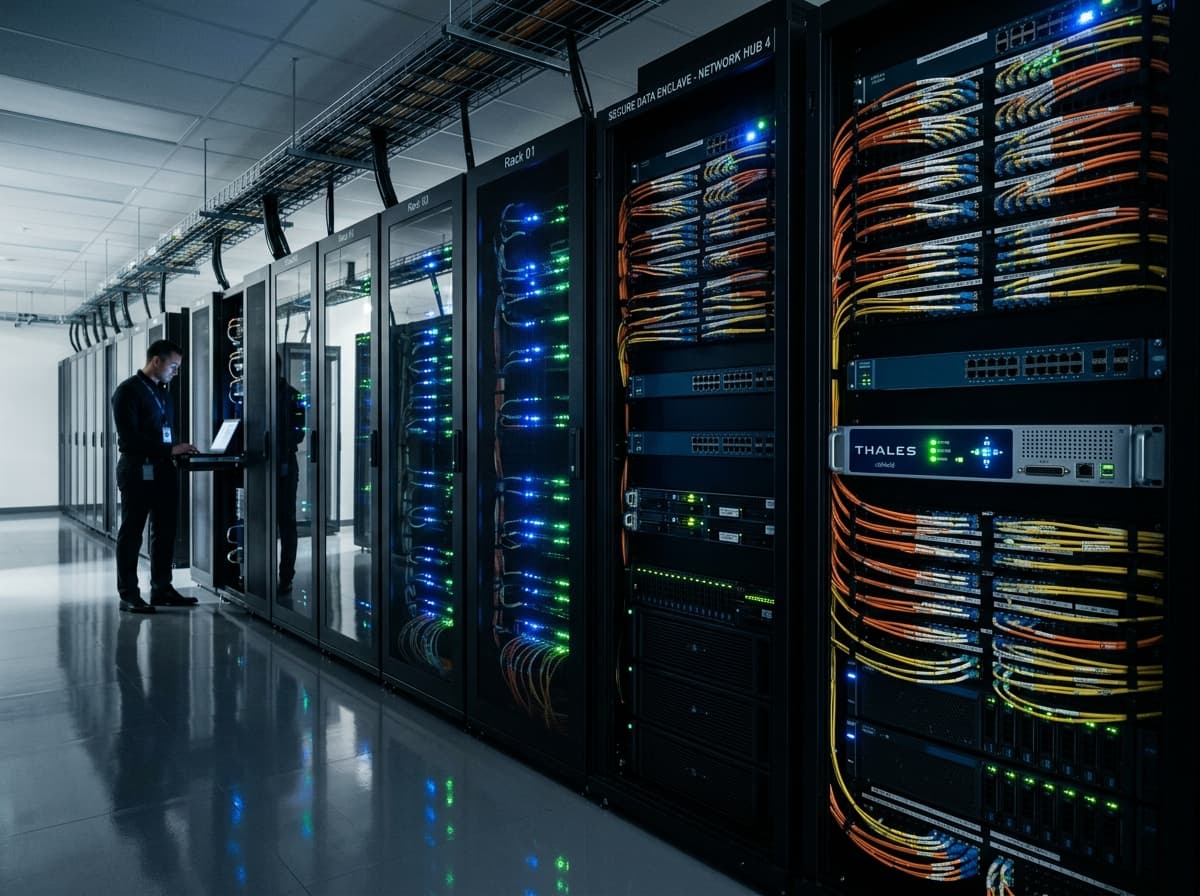
Sovereign On-Premise data centre deployment, certified private banking cloud, or hybrid distributed clearing nodes.
Complete Infrastructure Control in Your Bank Data Centre
Designed for scheduled banks and cooperative apex institutions requiring complete regulatory sovereignty, on-premise hardware control, and zero external dependency.
Schedule a Custom Platform Architecture Review
Connect with our senior banking systems architects for a detailed evaluation of your institution's CTS clearing, AI document extraction, or core banking interoperability roadmap.